Malicious Browser Extensions: The Trusted-Tool Blind Spot
A trusted extension can be sold overnight and turned into spyware, and most companies have no idea what’s installed on their fleet.
A trusted extension can be sold overnight and turned into spyware, and most companies have no idea what’s installed on their fleet.
A single compromised user account is rarely where an attacker stops. On Windows, the path from an ordinary login to complete system control is well-mapped and short.
Buying a penetration test is easier when you know what the week actually involves. Here is the shape of a real engagement, from the paperwork to the retest.
Email is still the front door to your business. Here is how to tell whether the service guarding it is actually doing the job.
Your security program stops at your firewall. Your risk does not.
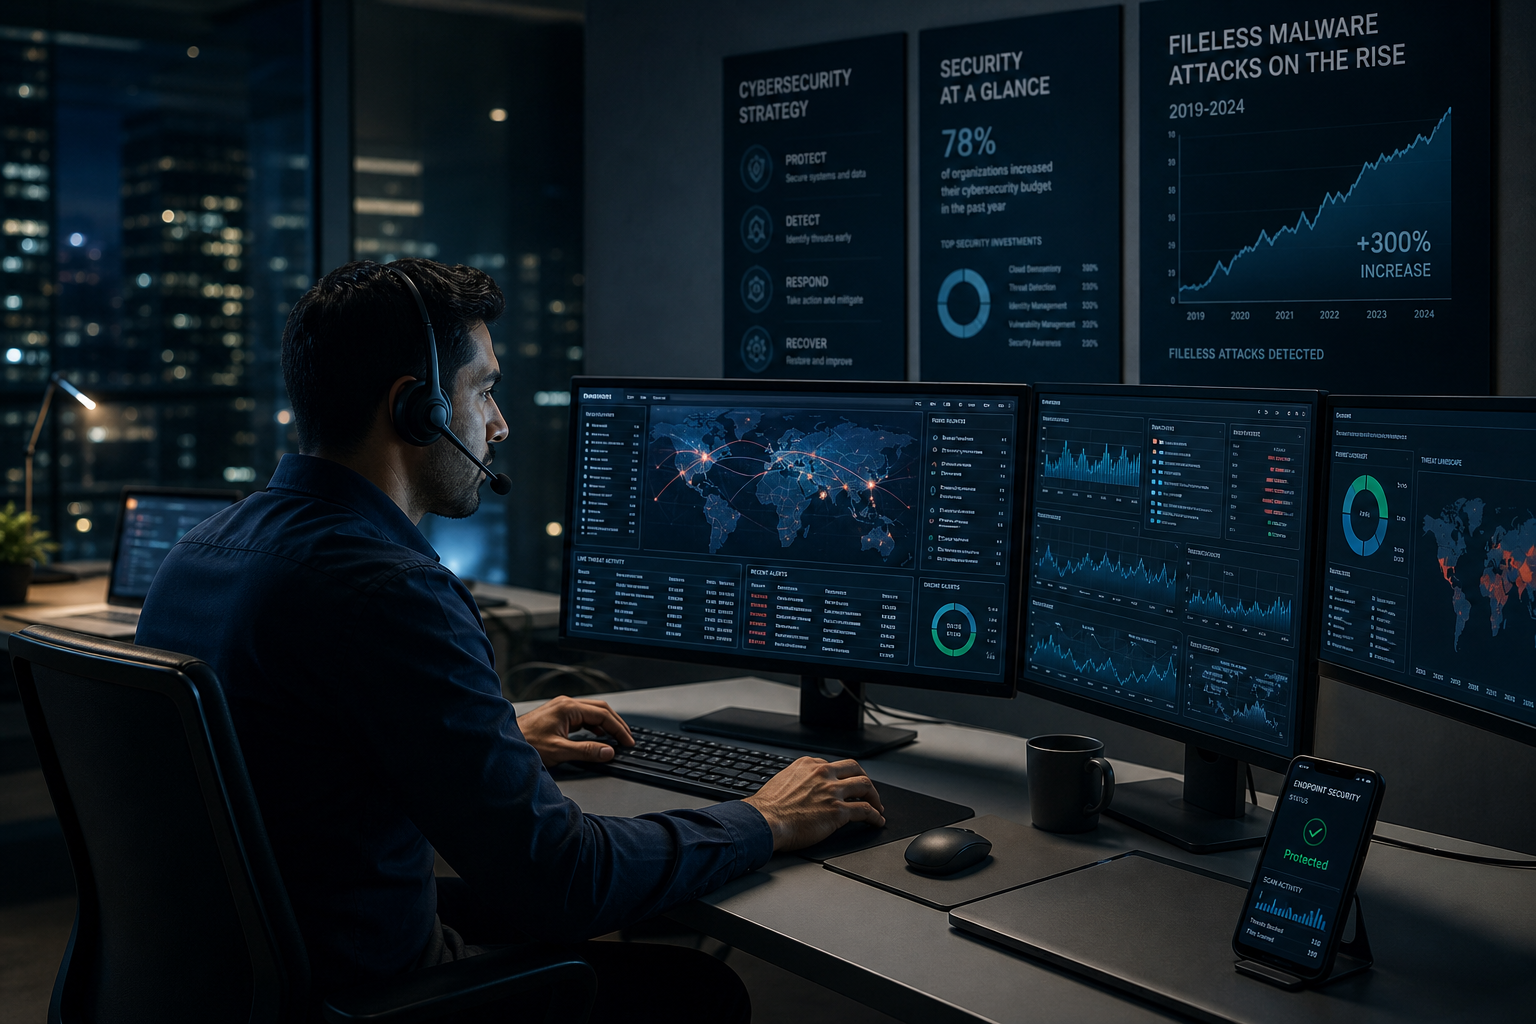
If your endpoint protection still works by recognizing known malware files, it is already a step behind the attackers who stopped using malware files.
Attackers are turning trusted Microsoft workflows against your users. And the quiet retirement of Defender’s built-in VPN is a good reason for every IT manager to look hard at what their bundled tools actually cover.
That PNG attachment in your inbox might be more than just pixels.
When Microsoft tells you to unplug your own servers, do not stop, do not pass Go and do not collect $200. Kindly proceed directly to your server room.
In my years of penetration testing and security consulting, I have learned two truths. First, vulnerabilities wait for no one. Second, if patching is not automated, it will be delayed, and those delays can eventually come back to bite you. I have lost count of the times a client said, “We will handle that next sprint,” only to find their systems...